Webhook Protection
Luarmor now offers an advanced webhook protection macro that you can use inside your script to prevent people from deleting, spamming or nuking your webhooks.
This feature is available in V4 loader scripts only. So make sure you enable the "Prefer V4 loader" option on dashboard while editing / creating a script.
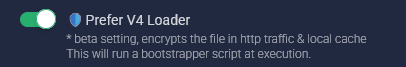
How to implement it in your script:
It is a macro, it means that you must include it in your script when you want to make a secure webhook request.
Syntax: LRM_SEND_WEBHOOK(<url constant>, <webhook template>)
It takes 2 arguments, first argument is a constant string literal that contains the webhook URL. Second argument is a constant table literal, containing the JSON payload of your webhook message.
Do not pass variables as arguments, it won't work. They must be constant.
There is also a sanitization macro, so people don't spoof the values coming from their client.
Syntax: LRM_SANITIZE(<any>, <regex string literal>)
Sanitize macro takes 2 arguments too. First one could be anything, variable, function call etc. Second argument must be a regex string without the / symbols at the start & end, and without anchors (^ / $).
E.g LRM_SANITIZE(plrname, "[a-zA-Z0-9_]{3, 40}")
Example usage:
if bounty > 45000 then
    -- Send high bounty player to webhook.
    LRM_SEND_WEBHOOK( "https://discord.com/api/webhooks/......", {
        username = "Cat Delivery",
        embeds = {
            {
              title = "High bounty user detected!",
              description = "Bounty: " .. LRM_SANITIZE(bounty, "[0-9]{1,6}"),
              color = 16711680, -- red

              fields = {
                  {
                      name = "Player Name:",
                      value = LRM_SANITIZE(plrName, "[a-zA-Z0-9_]{3,40}"),
                      inline = true
                  },
                  {
                      name = "Caught by:",
                      value = "<@%DISCORD_ID%>", -- Server-side variable, see below
                      inline = true
                  }
              }
            }
        }
    });

    print("Webhook sent!")
end
This code will safely send high-bounty players in some game and their names, with server-side regex sanitizations & server sided template rendering. Client only provides the "bounty" and "plrName" variables. Everything else happens on the server, client never knows.
Server-side Variables:
You can also use certain server-side variables, wrapped between % % in your template strings. They will get replaced at the server, and can not be spoofed / changed by user.
Here is a list:
%DISCORD_ID%
Discord ID of the user sending the webhook request.
11024175100150935723
%COUNTRY_CODE%
2 letter country code of the user IP at the time of execution
gb
%USER_KEY%
script_key value
SjZvGboZMJt .... (32 chars)
%CLIENT_IP%
IP v4/v6 of the user at the time of execution
48.72.104.256
%USER_NOTE%
Note, if the key has any.
Not Specified
You include them in the constant strings in the template, like:
Restrictions:
Last updated